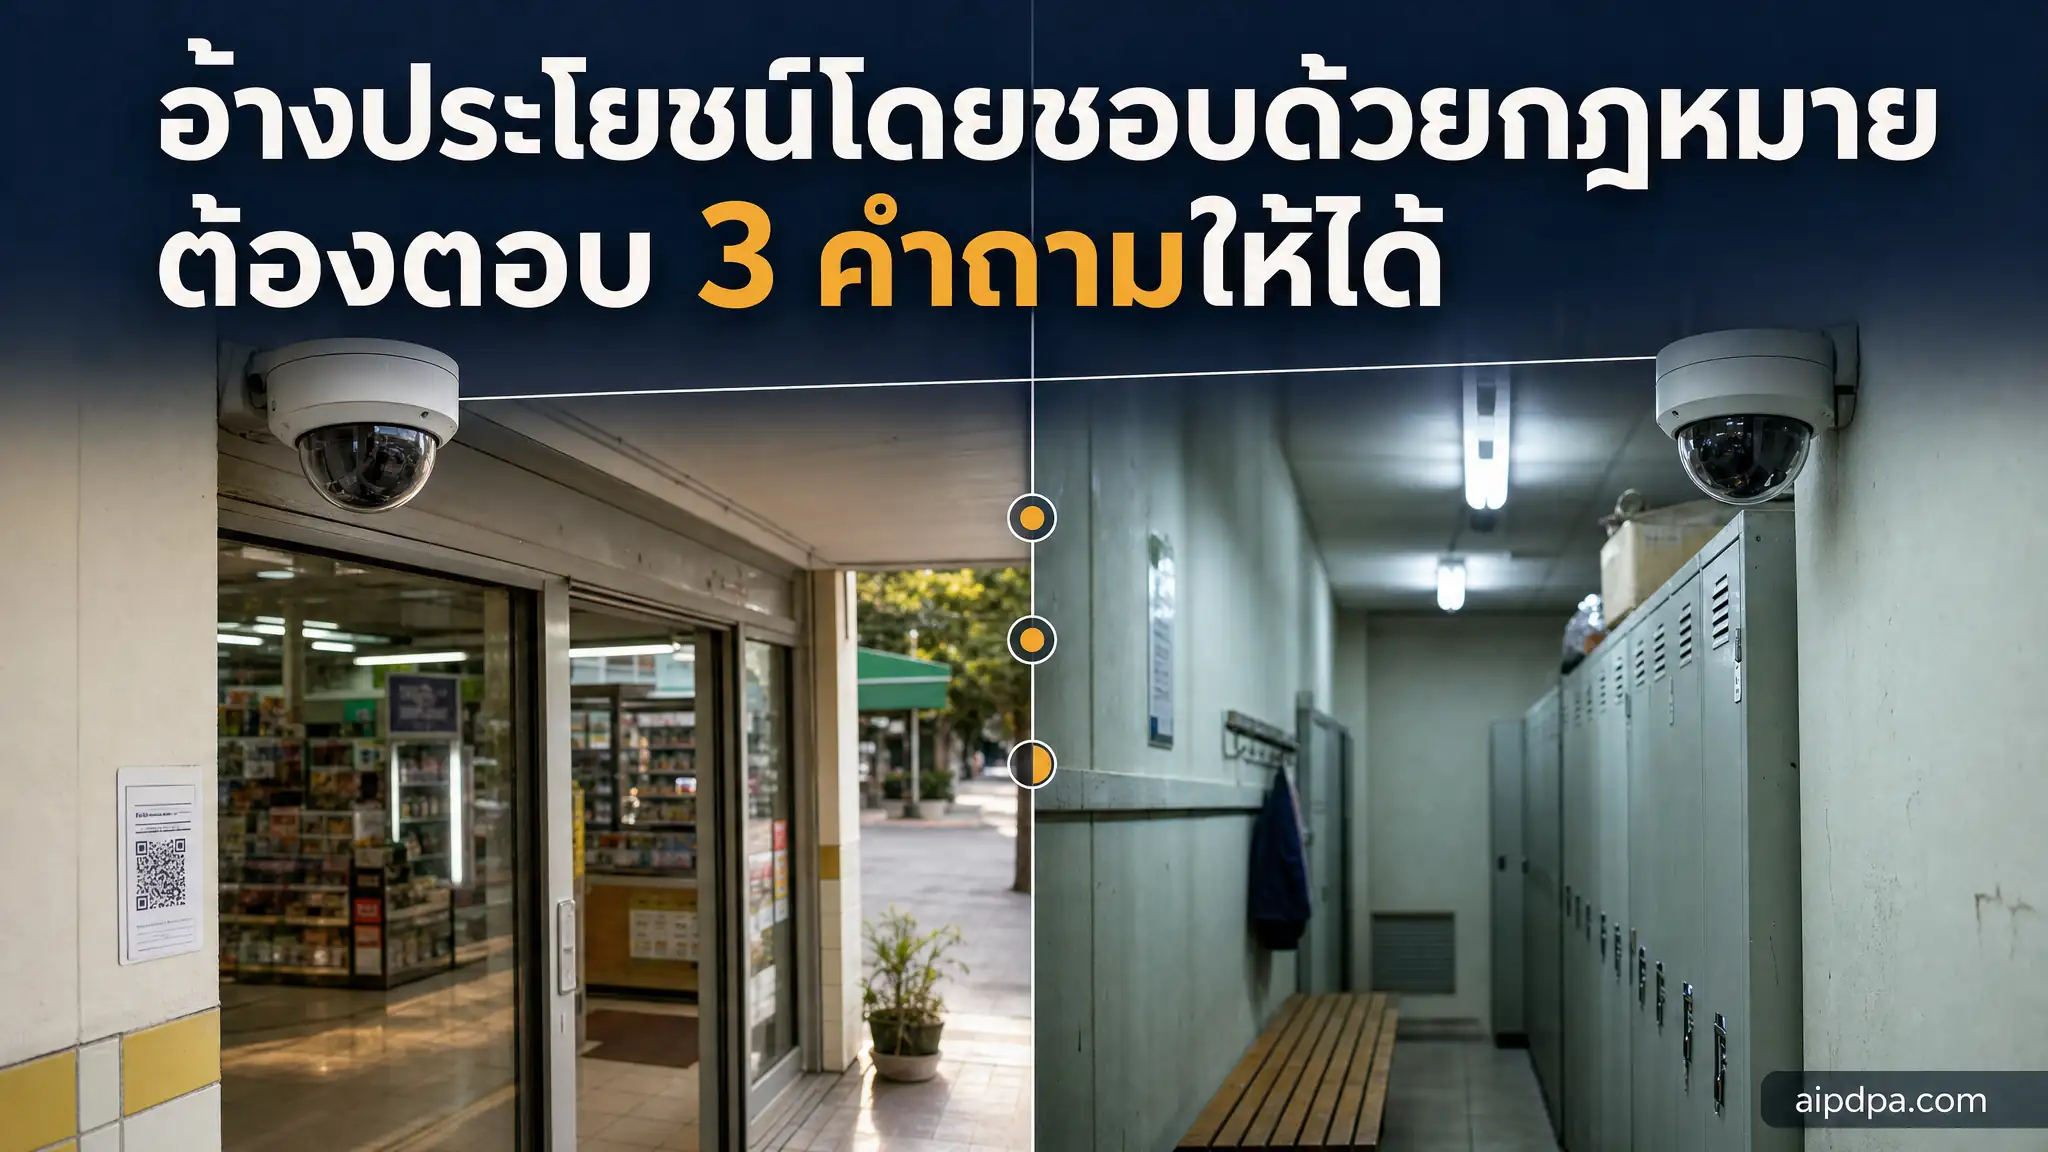
Relying on legitimate interest under section 24(5) of Thailand's PDPA means processing personal data without consent, provided the company can answer three questions: is the purpose legitimate, is the processing necessary, and does it unreasonably override the person's rights. This article is for DPOs and legal teams who must write an LIA record and decide whether common activities belong on this basis.
- Section 24(5) allows processing without consent when it is necessary for a legitimate interest that is not overridden by the data subject's rights.
- Before using it, answer three questions: is the purpose legitimate, is the processing necessary, and does it unreasonably affect the person?
- Sensitive data under section 26 cannot use this basis. Children's data sometimes can, but TDPG 4.0 asks for a stricter balancing test.
- People can object under section 32; the company must stop unless it proves a compelling legitimate ground, and must record any refusal under section 39.
- CCTV and fraud prevention usually pass. Marketing, staff monitoring and analytics need care. Targeted ads built on profiles need consent.
Plenty of Thai privacy notices contain one line that is meant to cover everything: "we process your data for our legitimate interests." It looks like the easiest basis in the law. Nobody has to tick a box, and nobody can withdraw consent that was never asked for.
Section 24(5) of the Personal Data Protection Act 2019 (PDPA) is less generous than that line suggests. The same sentence requires the processing to be necessary, and it stops working when the company's interest is outweighed by the data subject's rights. When a customer or employee objects, or the Office of the Personal Data Protection Committee (PDPC Office) asks for the reasoning, the company needs a written answer, not a feeling that it is probably fine.
This article breaks the basis into the three questions a company has to answer, shows which data cannot use it or needs special care, explains the right to object under section 32, sets out what an LIA record should contain, and ends with a frank first verdict on the activities Thai companies most often put on this basis.
What does section 24(5) allow, and on what conditions?
Section 24(5) allows a data controller to collect personal data without consent when this is necessary for the legitimate interests of the controller or of another person. The provision is a single short paragraph.
(5) it is necessary for legitimate interests of the Data Controller or any other Persons or juristic persons other than the Data Controller, except where such interests are overridden by the fundamental rights of the data subject of his or her Personal Data;
Read slowly, it has three layers. First, there must be a real legitimate interest. Second, the processing must be necessary, not merely convenient or cheaper. Third, after the word "except", the basis falls away if the data subject's fundamental rights weigh more.
TDPG 4.0 item C63 is blunt about the risk: because the basis is broad and flexible, the controller has to exercise considerable discretion, and a wrong call may leave it liable later. The flexibility that makes legitimate interest attractive is exactly why the reasoning has to be written down.
What are the three questions to answer before relying on it?
The questions are: what is it for, how necessary is it, and does it unreasonably affect the person. TDPG 4.0 cites a PDPC Office opinion recommending a Legitimate Interest Assessment (LIA) built on exactly these three criteria. If any one of them has no good answer, stop and look for another basis.
Question 1: is the purpose legitimate?
First, the Purpose Test: this considers the reasons and benefits to be obtained from the collection, use, or disclosure of such personal data, and whether and how it is lawful
A usable answer is specific enough for an outsider to check, such as "preventing shoplifting in our branches" or "detecting orders placed with stolen cards". Phrases like "for business administration" or "to develop our business" are too broad to test.
TDPG 4.0 item C62 lists interests that are commonly accepted, including crime and fraud prevention, transfers within a corporate group for internal administration (not abroad), and the security of systems and networks, always within the scope the data subject could reasonably expect.
Question 2: is it really necessary, or is there a less intrusive way?
Second, the Necessity Test: this considers how necessary the processing is in order to achieve that lawful purpose, and whether and to what extent it could be carried out by another method that would have a lesser impact on the personal rights of the data subject
This is the question that filters out the most activities, because it forces you to ask whether less data would give the same result. Do you need 90 days of footage, or would 30 do? Do you need to know who clicked, or only how many clicks there were? If a less intrusive method exists and you still pick the more intrusive one, the test fails.
The LIA table in TDPG 4.0 also asks whether the processing could be carried out on another lawful basis. If the activity already fits contract or legal obligation, use that basis directly rather than stacking legitimate interest on top.
Question 3: do the person's rights weigh more?
Third, the Balancing Test: this considers weighing the legitimate interest against the fundamental right in personal data of the data subject, which must not unreasonably affect the right to privacy of the data subject
Here you look from the data subject's side. TDPG 4.0 suggests asking whether the person could reasonably expect the processing, whether it benefits the service they use, and whether it could harm them. The more private the data, or the weaker the person's bargaining position, the more the scales tip toward them.
The usual trap is assuming that anything written in the privacy policy is, by definition, expected. TDPG 4.0 closes that door in item C64.
The data controller may not claim that the data subject should have been able to expect the data processing merely because it was stated in the privacy policy, if the content was not specific and there is no assurance that the data subject would actually have had an opportunity to read it
In practice, reasonable expectation comes from notice at the point of collection: a sign at the edge of the camera zone, a short line on the sign-up form, a sentence on the checkout page. A paragraph buried deep in a long policy does little for this question.
Which data cannot use this basis, or needs extra care?
Sensitive data under section 26 cannot rest on legitimate interest at all. Children's data sometimes can, but only with a stricter balancing test. The two are often lumped together, and they should not be.
Sensitive data: section 26
Any collection of Personal Data pertaining to racial, ethnic origin, political opinions, cult, religious or philosophical beliefs, sexual behavior, criminal records, health data, disability, trade union information, genetic data, biometric data, or of any data which may affect the data subject in the same manner, as prescribed by the Committee, is prohibited, without the explicit consent from the data subject, except where:
The exceptions that follow are five: preventing danger to life where the person cannot consent; activities of foundations or associations with their members; data made public with explicit consent; establishing or defending legal claims; and compliance with law for listed purposes. Legitimate interest is not on that list.
The clearest consequence involves cameras. If a company upgrades its lobby cameras from plain recording to face recognition, the output falls within "biometric data" as defined in section 26 paragraph two, which names facial recognition data as an example. An LIA written for ordinary CCTV does not carry over; the company needs a section 26 exception or explicit consent.
Children's data: section 20
Section 20 sets out how consent is obtained from minors. It does not forbid legitimate interest for children's data, but its fourth paragraph extends the parental rules to notices and the exercise of rights as well.
The provisions of paragraphs one, two, and three shall apply mutatis mutandis to the withdrawal of consent of the data subject, the notice given to the data subject, the exercise of rights of the data subject, the complaint of the data subject, and any other acts under this Act for the data subject who is a minor, an incompetent or quasi-incompetent person.
So even without consent, the notice and the route to object have to be designed with parents in mind. For the balancing itself, TDPG 4.0 cites European Data Protection Board (EDPB) guidance that gives children extra weight.
In the case of processing data of minors, the interests of minors shall receive special protection and be given the highest importance, since minors are less aware of the risks, impacts, and safeguards related to the processing of personal data, and the rigor and thoroughness of the balancing test should be adjusted to be even greater
The careful route is to have a person decide every LIA that touches minors, such as learning apps, membership schemes children can join, or photos of school events, rather than letting a form produce the answer. Age thresholds are covered in our guide to children's data under section 20.
What must a company do when someone objects?
Stop and separate the data straight away, unless it can prove a compelling legitimate ground or a legal claim. Section 32(1) gives the right to object specifically to data collected under section 24(5).
(1) Where the Personal Data is collected with the exemption to consent requirements under section 24 (4) or (5), unless the Data Controller can prove that: (a) the collection, use, or disclosure of such Personal Data can be demonstrated by the Data Controller that there is a compelling legitimate ground;
In the event that the data subject exercises his or her right to object in paragraph one, the Data Controller shall no longer be able to collect, use, or disclose such Personal Data, and the Data Controller shall immediately distinguish such personal data clearly from the other matters at the time when the data subject gives the notice of objection to the Data Controller.
The words "can prove" put the burden on the company, not on the person objecting. If the company refuses an objection, section 32 paragraph three requires the refusal and its reasons to be logged in the section 39 record, and section 39 lists it as a mandatory entry.
(7) the rejection of request or objection according to section 30 paragraph three, section 31 paragraph three, section 32 paragraph three, and section 36 paragraph one;
Direct marketing is stricter still. Section 32(2) makes objection to direct marketing a separate case, with no wording that lets the company prove an overriding ground as in (1), and TDPG 4.0 cites EDPB guidance that processing must stop immediately once someone objects.
What should an LIA record contain so it can be checked?
An LIA record should answer the three questions in writing, name who decided, and set a review date. The PDPA prescribes no LIA template, so the headings below are good practice rather than a legal requirement, but each one traces back to a question in the Act or in TDPG 4.0.
| Heading | What to write | A checkable example |
|---|---|---|
| Activity and owner | Activity name matching the RoPA line, and the team responsible | Branch CCTV · Facilities team |
| Purpose (question 1) | The benefit, and whose benefit it is | Prevent theft and keep evidence of incidents in store |
| Data and people | Data types and who is captured | Video of customers and staff on the shop floor; no audio |
| Necessity (question 2) | Less intrusive options considered, and why they were rejected | Extra guards considered, but they do not cover closed hours |
| Balancing (question 3) | People's expectations, impact, and vulnerable groups | Sign at the entrance; no cameras in toilets or changing rooms |
| Safeguards | Who can view, how long it is kept, how it is protected | Auto-delete after 30 days; playback by branch manager only; viewing log kept |
| Notice and objection | Where people are told, and how they object | Sign with a QR code to the full notice; DPO email |
| Outcome and decision-maker | Pass, pass with conditions, or fail, with name and date | Pass with conditions · signed by the DPO on 3 November 2026 |
| Review | Review cycle, and triggers for an early review | Every 12 months, or when face analysis or audio is added |
The last two rows matter more than they look. An LIA without a named decision-maker belongs to nobody, and one without a review date stays frozen on the old version of the activity, even after four cameras have quietly become forty.
In AIPDPA, the LIA flow sits inside the RoPA register: 3 parts and 15 questions (14 required), with answers pre-filled from the register. Activities involving sensitive data, minors or automated decisions are never auto-decided; they go to a person. AI only pre-fills, and can only make the result more cautious. If the person's decision differs from the system's suggestion, they must write a reason. The output is a numbered LIA record valid for 12 months, on every plan.
How far does this basis go for everyday activities?
The verdicts below are a practitioner's reading of the Act alongside TDPG 4.0, not PDPC decisions. Real outcomes depend on each organisation's facts, so treat them as the starting point for an LIA, never as a substitute for one.
TDPG 4.0 Chapter E gives CCTV as an example on the legitimate interests basis and recommends an LIA, limited camera angles and short retention. The verdict changes for very private areas, audio, or face analysis.
Item C62 names fraud prevention as a typical interest, but the EDPB guidance cited in TDPG stresses it must be strictly limited to what is necessary and pass both the necessity and balancing tests.
Item C39 and the PDPC Office bank opinion allow it where it is not intrusive and customers expect it, but item C35 makes consent the main basis for direct marketing, and an objection ends it.
TDPG accepts transparent tracking of hours worked for billing and bonuses, but finds covert monitoring of staff browsing history cannot rely on this basis.
The example under item C11 says behaviour analysis is not contractual necessity and points to consent or legitimate interest instead, so it must be weighed case by case.
Item C39 says targeted advertising that relies on individual data or profiling cannot use legitimate interest and must use consent.
Facial recognition data is biometric data under section 26, which offers no legitimate interest exception.
Marketing to existing customers: TDPG pulls in two directions
TDPG 4.0 item C35 says direct marketing must rely primarily on consent, while item C39 leaves room where the marketing is not very intrusive and customers already expect it. The two items have to be read together.
Direct marketing that is not highly intrusive on privacy and that consumers can already reasonably expect may use the legitimate interest basis, such as sending product information to customers registered as members of a supermarket. However, directly offering products for sale or targeted advertisement that relies on specific individual data, or profiling data that enables the advertiser to know detailed personal data about the target, cannot use the legitimate interest basis and must use the consent basis.
The PDPC Office opinion that TDPG cites on banks offering ATM cards or mobile banking to deposit customers points the same way: the bank may consider this basis by weighing customer expectations and proportionality, may keep an LIA as part of its records, and should tell customers they can object.
A workable line: products close to what the customer already uses, sent at a modest frequency with an easy way out, can be balanced. Turning individual behaviour into targeted ads needs consent. For more on customer lists and cookies, see marketing lists and cookies.
Employee monitoring: the example TDPG says fails
TDPG 4.0 sets two examples side by side. Recording consulting lawyers' hours to calculate costs and bonuses can rely on this basis, because the system is transparent and staff can challenge it. A company that monitors staff internet use, including browsing and download history, cannot.
This monitoring was carried out without informing employees or the labor union in advance, and without clearly informing them of the details of the data processing. In such a case, even though the company has a legitimate interest, it substantially conflicts with the employees' right to privacy, and the data collection may also be carried out beyond what is necessary, disproportionate, and not transparent. In addition, there are other methods that would infringe the employees' rights less, such as restricting access to certain types of websites from company computers. It therefore cannot rely on the legitimate interest lawful basis
The example fails questions 2 and 3 together: the purpose is reasonable, but a gentler method exists and staff had no idea. For employers the lesson is to tell people first, collect only what is used, and block sites before logging individuals. The wider picture is in our employee data guide.
Which mistakes make an LIA worthless?
- Writing the LIA after launch, just to have a document when asked. It reads as a justification, not a real weighing.
- One LIA for every activity, although the data, the people affected and the alternatives differ each time.
- Relying on the privacy policy alone, which TDPG 4.0 item C64 rejects when the content is not specific.
- No less intrusive alternatives written down, which leaves question 2 empty and impossible to check.
- Using this basis for biometric, health or criminal record data, for which section 26 provides no such exception.
- No channel for objections and nowhere to log refusals under section 39(7).
A good LIA does not have to be long. It has to show who decided, on what reasoning, and when it will be looked at again. To start with what outsiders already see, run the free website scan, which produces a PDPA and security report for your site, and check whether your privacy notice states the basis and the right to object. The step-by-step method is in our LIA guide.
Frequently asked questions
Do we need PDPC Office approval before relying on legitimate interest?
Section 24(5) does not require approval or any filing with the PDPC Office. The company must be able to explain its reasoning when asked, and when someone objects, section 32(1) puts the burden of proof on the company. That is why the LIA record should exist before the activity starts.
How is an LIA different from a DPIA?
An LIA answers whether legitimate interest is an available basis. A DPIA assesses the overall risk of an activity to people's rights. One activity can need both: TDPG 4.0 recommends an LIA for CCTV and an additional DPIA when audio recording or face analysis is used.
Can we use legitimate interest for employee health data?
No. Health data falls under section 26, which requires explicit consent unless one of its exceptions applies, such as compliance with labour protection law under section 26(5)(c). None of those exceptions is legitimate interest.
A customer objected to promotional email. May we keep their name?
Stop the direct marketing at once under section 32(2) and paragraph two. TDPG 4.0 gives an example where a company may rely on legitimate interest to keep the name and contact details of someone who opted out, so that newsletters are not sent to them again.
How often should an LIA be reviewed?
The Act sets no interval. Good practice is a fixed cycle, such as once a year, plus a review whenever the activity changes: new data types, new technology, or new recipients. TDPG 4.0 itself recommends periodically reviewing the LIA for event photography.
Law and sources
- Personal Data Protection Act B.E. 2562 (2019) — Section 20 · Section 23 (6) · Section 24 (5) · Section 26 · Section 32 · Section 39 (7)
- TDPG 4.0 Thailand Data Protection Guidelines (guidance, not law) — C35 · C39 · C62–C65
Text in the "The text" boxes is copied word for word from AIPDPA's legal knowledge base, transcribed from the Royal Gazette and official documents; every edit is checked by the system against that base, character by character. English wording is an unofficial translation; the Thai text prevails. This article is general information, not legal advice for a particular case.
Do it in the system
Who stands behind this guide?
Written by the AIPDPA legal team · Content owner: Phuwara Krobtaku, Attorney-at-law · Thai Barrister-at-Law · technology & intellectual property counsel
Lawyer's licence no. 477/2558 · Thai Barrister-at-Law · LL.M. in Intellectual Property & IT Law (Gold Medal)